Proper Tagging and Labeling of Evidence in Digital Forensics


Blog Overview: Proper Tagging and Labeling of Evidence helps investigators in identification of each evidence item, document where it came from, keep it traceable, and manage it correctly during an entire investigation. For digital evidence, same principle extends to devices, forensic images, files, emails, and other extracted artifacts.
Label should simply tell us:
- What is this evidence,
- Where it come from
- Which case it belong to.
Good and clean tagging goes step further that helps investigators classify, organize, search, and retrieve relevant evidence during examination.
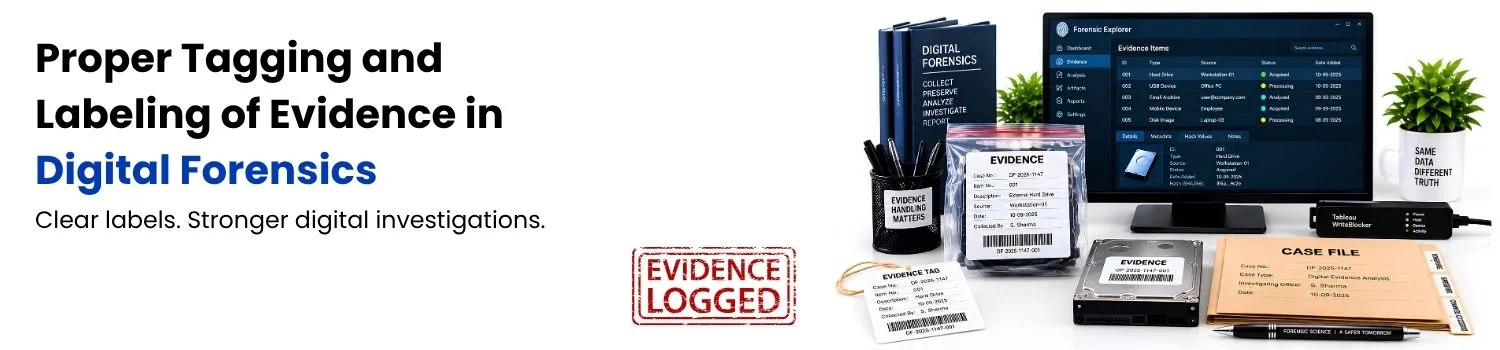
Therefore, in this article, you will get to know how email tagging software works during the investigation process. Here, we will also give you the best techniques and tips to do proper evidence labeling and tagging to mark evidence.
Proper identification is important because evidence moves from collection, packaging, storage, transfer, acquisition, examination, and reporting. NIST describes digital forensics as identification, collection, examination, and analysis of data through preserving its integrity and maintaining proper chain of custody.
Why Proper Evidence Tagging Is Important
Proper evidence tagging gives every item clear identity before it becomes one item among hundreds or thousands. It reduces confusion, supports consistent documentation, and helps investigators connect an item to the right case, source, and handling record. Proper evidence tagging provided identity to every item. Before it becomes an important item among hundreds or thousands.
Value becomes more clearer when evidence changes hands and move between systems. Well-documented evidence record can clearly show:
- What was collected.
- When it was collected.
- Where it was found.
- Who handled it.
- Where it was found.
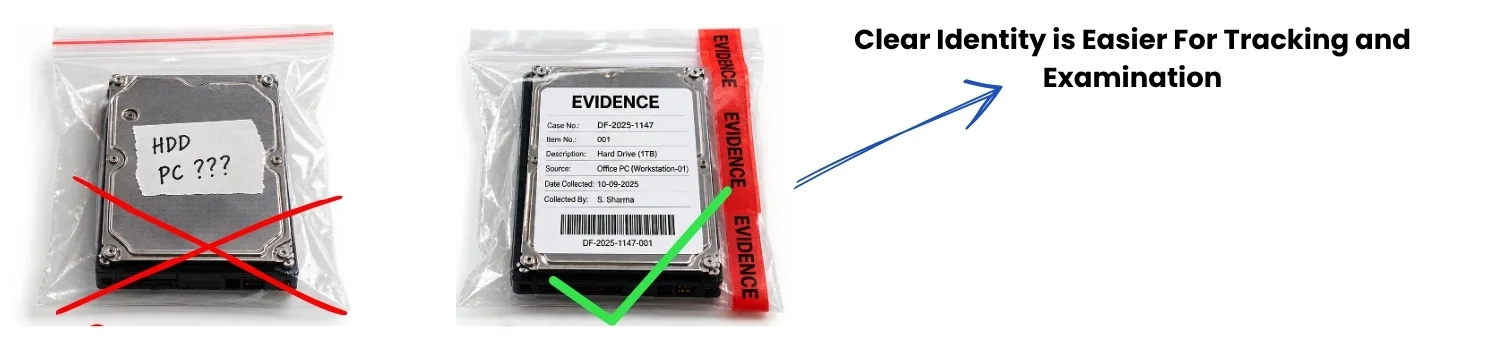
One way to think about it is simple: No clear identity is higher chance of confusion. Clear identity is easier tracking and examination. This is the reason proper tagging and labeling of evidence is important.
What Should an Evidence Label Include?
Good evidence label contains enough information to identify the item without forcing another person to guess what it is. Exact requirements differs by agency, laboratory, case type, and jurisdiction, so organization’s evidence-handling policy should take priority. Common information includes:
| Information | Why It Matters |
|---|---|
| Case number | Connects item to the investigation. |
| Item number | Gives evidence a unique reference. |
| Item description | Identifies what was collected |
| Collection date and time | Establishes when item entered custody. |
| Collection location | Documents where it was found. |
| Collector Identification | Identifies who collected it |
| Manufacturer model | Helps identify device or media. |
| Serial Number | Provides device-specific identifiers. |
| Condition or notable markings. | Records relevant observation. |
| Package and container information | Connects item to its packaging. |
Tagging vs. Labeling vs. Marking
These terms are closely related, but they are not interchangeable. Let us look each turn by turn.
- Tagging: Refers assigning information or categories that helps in identification, classification, organizing, or retrieve evidence.
- Labeling: This means recording identified information on the evidence, its container, or associated documentation.
- Marking: It means applying an identifying mark on an evidence itself when method is appropriate.
- Chain of custody: It records movement, handling, transfers and storage of evidence over time. NIST defines chain of custody as process that tracks evidence through collection, safeguarding and analysis by documenting handlers and relevant transfer details.
Now we will look at how to do proper tagging and labeling of evidence.
How to Properly Tag and Label Evidence
Safest approach is to treat identification as process rather than something added at the end.
1. Assign Unique Case and Item Identifier:
Start with consistent identifier that connects evidence to the correct investigation. Case number identifies investigation. Item number identifies specific evidence item within that case.
For example:
-
Case: DF-2026-014
-
Item: E-003
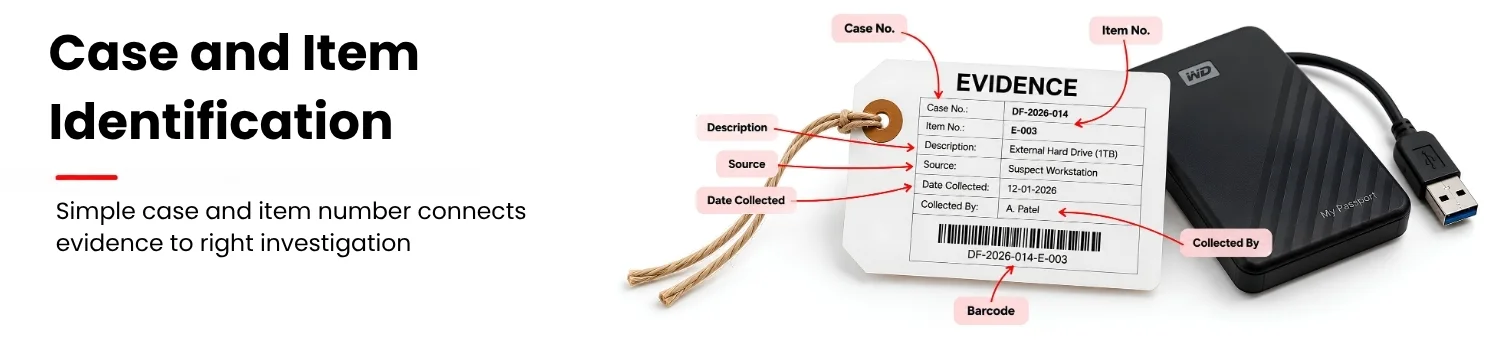
That simple combination makes it easier to distinguish one evidence item from another.
2. Record What Evidence Is:
Use clear and well thought-out description rather than vague label.
Instead of:
“Device“
use:
“Black Samsung smartphone, cracked screen, 256 GB storage.“
For storage device, record useful identifiers such as manufacturer, model, capacity, and serial number when available. Goal is not to write an essay. Goal is to make the item recognizable without ambiguity.
3. Record Where and When It Was Collected
Collection context matters. Record date, time, location, and relevant source information according to your organization’s norms. For digital evidence, source may be workstation, phone, removable device, mailbox, cloud account, or another system. This information helps connect evidence item to event in which it was acquired.
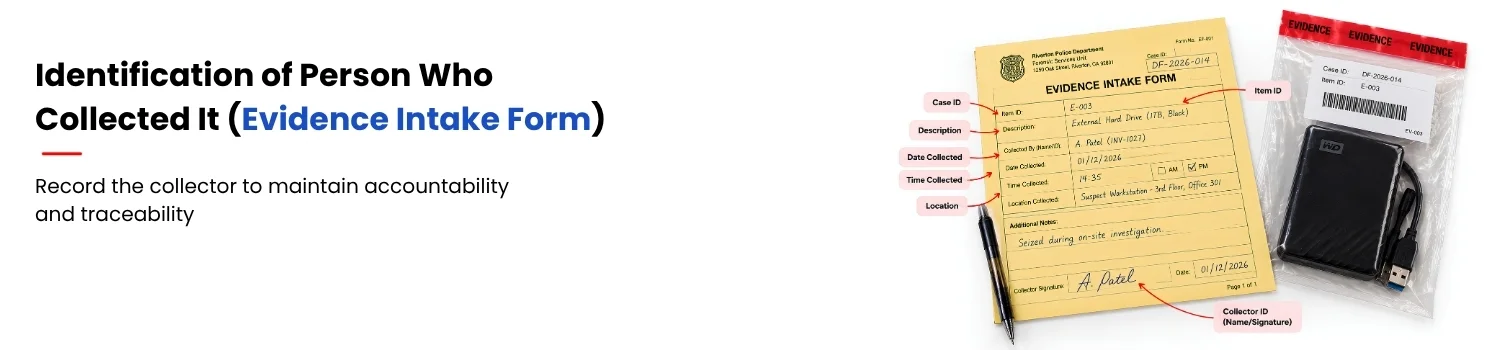
4. Identify Person Who Collected It
Evidence record should identify collector according to agency or laboratory’s required procedure. This helps in creation of accountability and supports larger custody record. NIJ guidance includes identity of the person who collected the item as part of the chain-of-custody information.
Related Read: How to Investigate a Suspicious Email
Label Evidence Without Hiding Its Existing Identity
Digital devices contain important manufacturer labels, serial numbers, model numbers, or regulatory markings.
Never cover or damage any information that can be useful for identification. SWGDE (Scientific Working Group on Digital Evidence) advises that evidence labeling should not cover existing identifying information, integral components, or existing labels.
Where direct marking is unsuitable, label the package or container instead, following the organization’s procedure in proper tagging and labeling of evidence.
Package and Seal Evidence Correctly
Labeling is only one part of evidence handling. Item needs appropriate packaging, sealing, and documentation. The specific packaging method depends on the type and condition of the evidence. For instance sealed evidence bag can show case number, item number, and description, with the required initials and date marked across seal.
Example
Case: DF-2026-014
Item: E-003
Description: External hard drive
Seal: Initials + date across seal
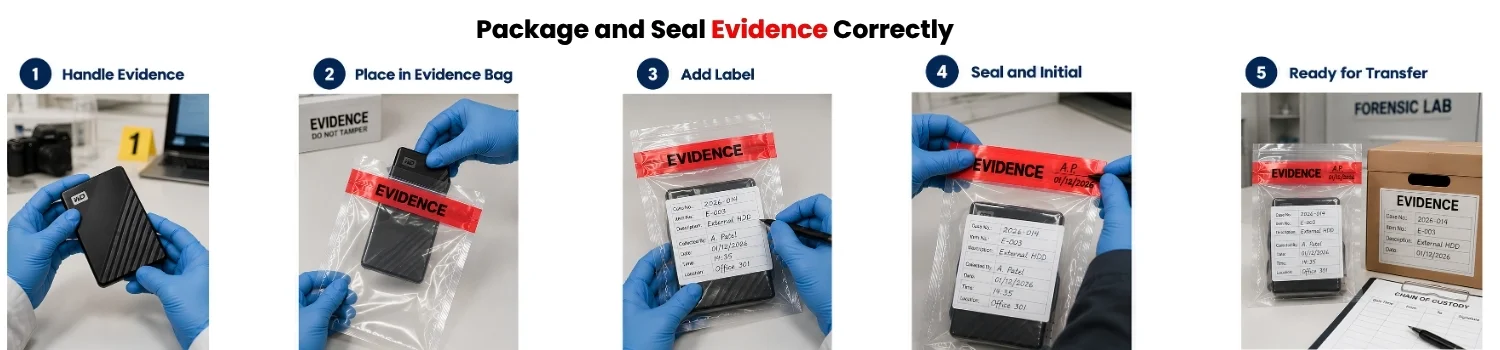
For digital devices, the priority is to package and preserve the evidence according to the applicable forensic procedure rather than treating every device the same way.
Related Read: Admissibility of Digital Evidence in the Court
Record Every Transfer
Proper tagging and labeling of evidence leads to a good chain of custody record. When evidence moves from one person, location, or controlled system to another, transfer should always be documented according to the applicable procedure. Documenting handlers and obtaining a transfer record or secure electronic transfer when custody changes. This creates continuous history rather than collection of disconnected labels.
Think of it this way:
- Label: What is this.
- Tag: How do I classify or find it.
- Chain of custody: Who had it, when, and what happened to it.
Keep the Naming System Consistent
Strong evidence system uses predictable naming. For example: DF-2026-014-E003
This can identify one evidence item consistently across an evidence log, forensic image, examination notes, report, and related records, provided that naming convention matches organization’s procedure. Consistency matters because evidence may exist in several forms:
- Original device
- Forensic acquisition
- Image
- Extracted artifacts, findings
The identifiers should make relationships easy to understand.
Tag Digital Evidence During Examination
Proper tagging and labeling of evidence in digital forensics introduces another layer of organization. Physical hard drive may contain one evidence identifier, while the examination can produce thousands of potentially relevant files, emails, attachments, browser artifacts, messages, and other records.
These can be organized with meaningful tags such as:
- Relevant
- Financial
- Communication
- User Activity
- Timeline
- Case Lead
Exact tag names should reflect investigation and organization’s workflow.
Goal is simple: Turn large evidence set into an organized collection that can be searched and reviewed efficiently.
NIST describes collection in computer and network forensics as including the identification, labeling, recording, and acquisition of relevant data while following procedure.
Apply Tags That Explain Why an Artifact Matters
Tag becomes useful when it communicates meaning. Consider email that contains a transaction instruction.
- A weak tag might be: Email 27
- Useful classification could be: Financial Investigation
With a supporting note such as: Transaction instruction related to account activity under review.
Second approach gives examiner context without changing underlying evidence. This is especially valuable when several investigators or reviewers examine the same evidence later.
Labeling Forensic Evidence in a Right Way!
The process of labeling forensic evidence is now added to the known forensic tool MailXaminer. The software provides this feature to effortlessly label forensic evidence in the email files to ease out the investigation process. By this, it becomes easy to analyze the data and add or remove labels with each file.
This is a result-oriented email forensics tool that can be used not only by tech-savvy users but also by users having less technical expertise. All because of its simplified user interface and countless features. This tool allows the investigation officers to diligently examine the crime scene and simplify the process.
Here’s How to Tag Email Files
While undergoing the investigation process, digital data classification is done by proper tagging and labeling of evidence. This software provides the functionality to add or remove evidence labels, tags from the data files. Follow the procedure for evidence tagging with any of the processed files:
- When a user opens the file into the software, it will get the data files on the screen. Just mark the files to which the user wants to add the information. Then, right-click and choose to Add Tag for labeling forensic evidence.
ADD TAG: – It provides the facility to add a new tag to the data file.
- This tool also allows us to remove or delete the existing tag from the data files.
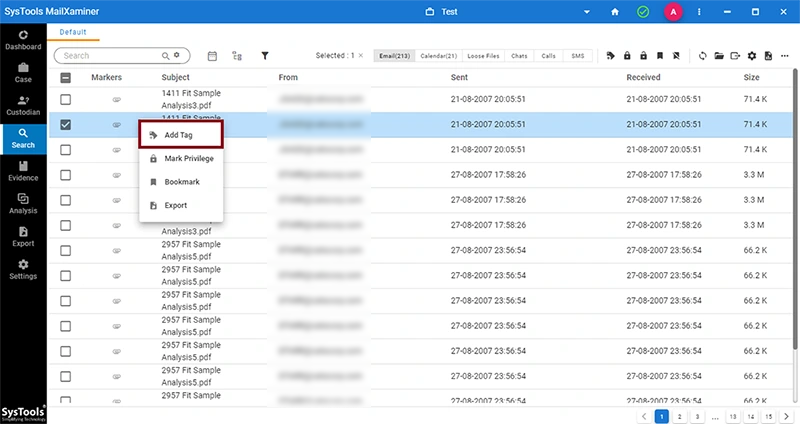
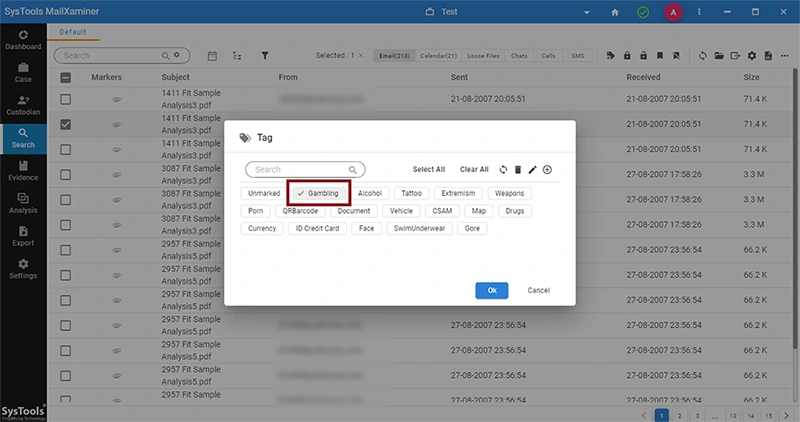
- In proper tagging and labeling of evidence, software allows to add new tag by clicking on Add Tag option. A pop-up window will display having the following fields i.e. Tag Name and Tag Description.
Tag Name:- Specify the name for the Tag.
Tag Description:- Describe the information related to the email content.
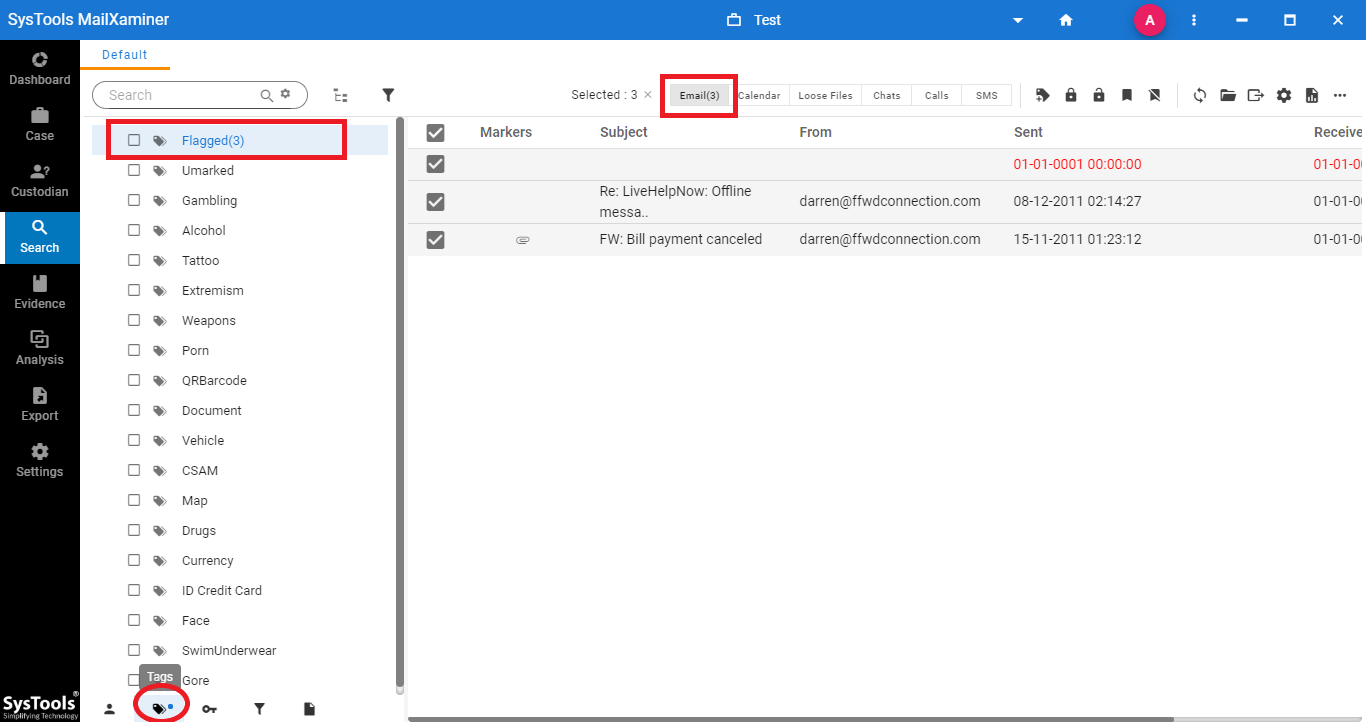
- In order to search the tagged information, opens the Tags tab. The screen will display the tagged data with specified tags and information. It allows to easily search of specific information to the investigators. To see evidence under any particular tag, just find the tag from the list and click on it.
7 Common Evidence Tagging and Labeling Mistakes
The problems are often simple mistakes. Mistakes that happens when investigators and collectors do not do proper tagging and labeling of evidence.
- Using vague descriptions: “Device” or “File” tells the next examiner very little.
- Missing identifiers: Without clear case or item reference, connecting evidence to the correct investigation becomes harder.
- Inconsistent naming: Different names for same item create unnecessary confusion.
- Covering existing identifiers: New label should not hide manufacturer’s serial number or another important marking.
- Treating tagging as chain of custody: Software tag or label do not replace documented history of possession and transfer.
- Over-tagging: Adding dozens of overlapping tags can make evidence harder, not easier, to review.
- Under-documenting context: A tag that says “Important” provides little value if nobody knows why the item is important.
Wrapping Up
Proper tagging and labeling of evidence is about traceability. At any point in investigation, another authorized person should be able to know:
- What evidence is,
- Which case it belongs to,
- Where it came from,
- How it relates to documented evidence record.
For digital evidence, traceability continues into examination. Physical device lead to a forensic acquisition, which produce files, emails, metadata, and other artifacts. Clear identifiers and meaningful tags help investigators maintain that relationship as the evidence is examined.
Frequently Asked Questions
Q: What information should an evidence label include ?
A – It includes the case number, item number, description, collection details, and collector information, based on the applicable procedure.
Q: Why is proper tagging and labeling of evidence important?
A – It helps identify, organize, track, and retrieve evidence while supporting proper documentation and chain of custody.
Q: What is the difference between tagging and labeling evidence?
A: Labeling identifies evidence or its package, while tagging helps classify, organize, or retrieve evidence during examination.